
Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution
The advisory, in context
Summary
A vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double file:// scheme (e.g., file://file:////). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads.
Note that this will only work if you have an authenticated administrator account with allowAdminChanges enabled.
https://craftcms.com/knowledge-base/securing-craft#set-allowAdminChanges-to-false-in-production
Details
The issue lies in line 57 of cms/src/helpers/FileHelper.php, it only removes file:// on the most left. It is trivial to bypass this sanitization by adding 2 file://, e.g. file://file:////.
    public static function normalizePath($path, $ds = DIRECTORY_SEPARATOR): string
    {
        // Remove any file protocol wrappers
        $path = StringHelper::removeLeft($path, 'file://');

        // Is this a UNC network share path?
        $isUnc = (str_starts_with($path, '//') || str_starts_with($path, '\\\\'));

        // Normalize the path
        $path = parent::normalizePath($path, $ds);

        // If it is UNC, add those slashes back in front
        if ($isUnc) {
            $path = $ds . $ds . ltrim($path, $ds);
        }

        return $path;
    }
PoC
- Sign in with an admin account and navigate to
Settings → Assets, then create a new volume. - n the Asset Filesystem section, create a new file system and set the Base Path to
file://file:////vendor. Without the prefix, the selection fails.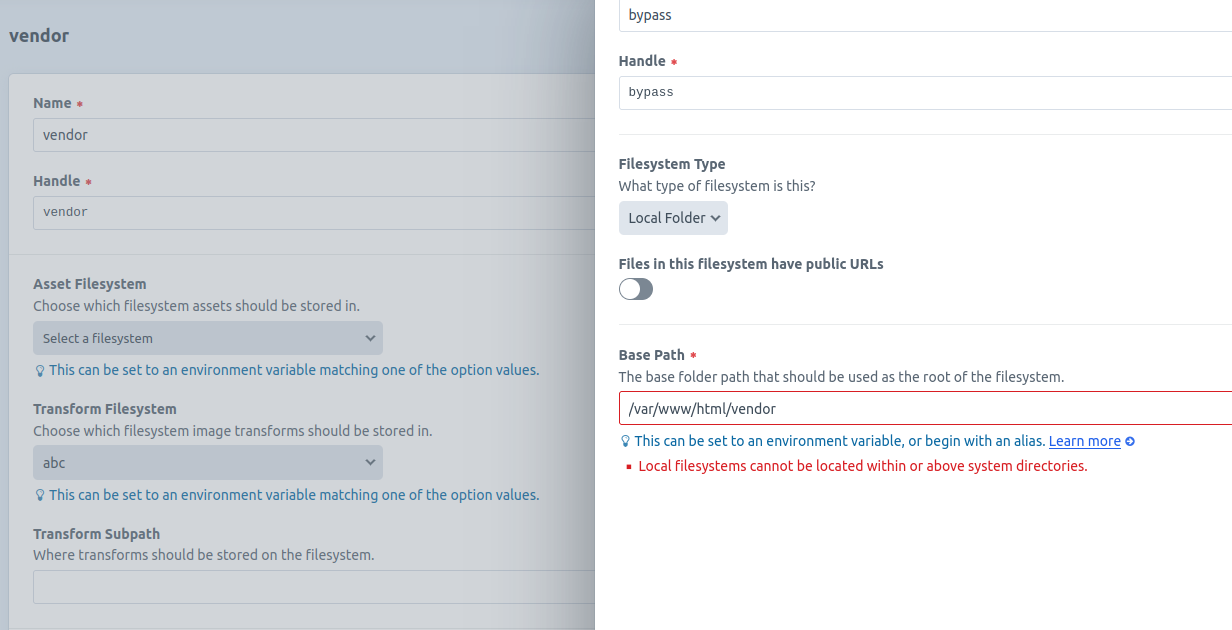 With the double
file://prefix, the selection succeeds.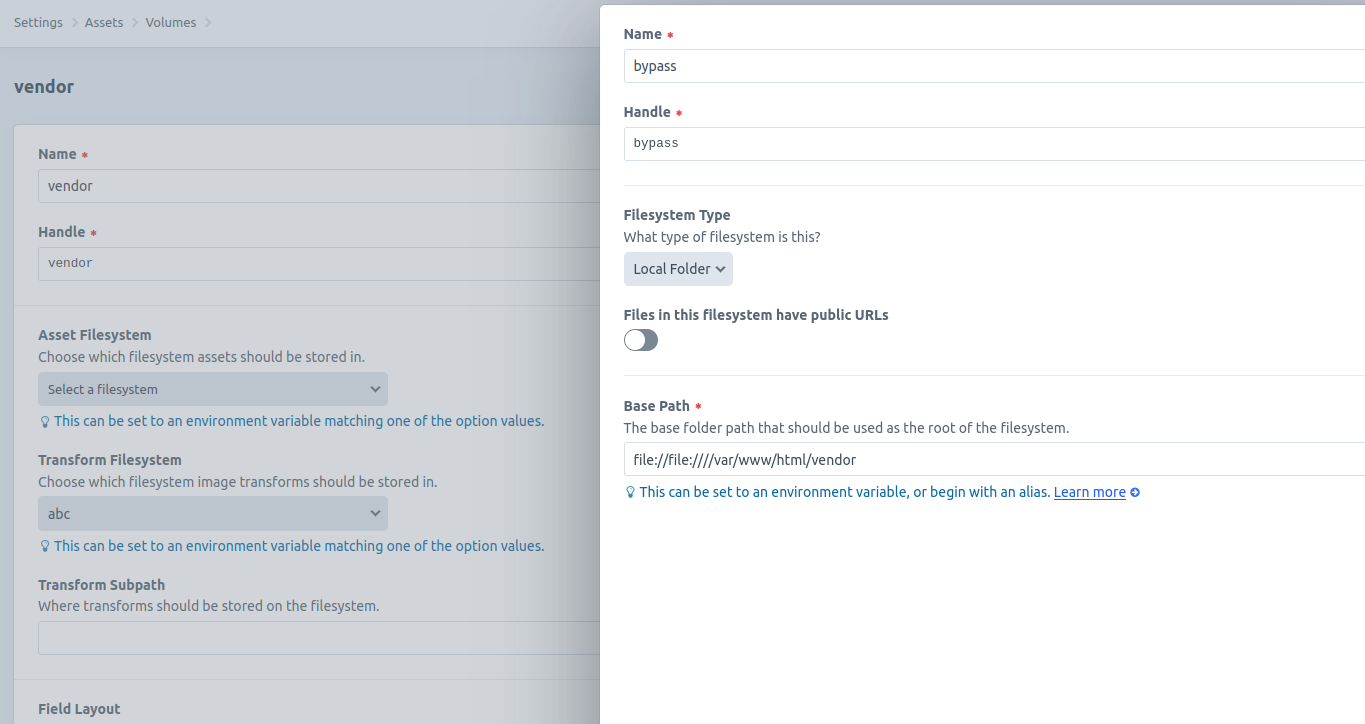
- Access Assets from the left navigation bar, then upload a file into this volume.
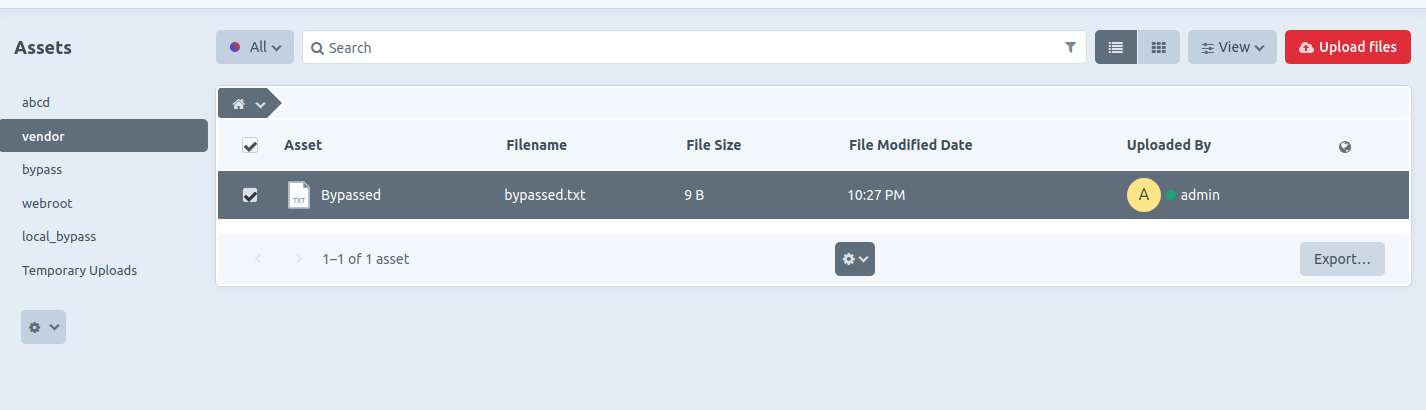
- The file is successfully uploaded and stored in the sensitive folder specified (e.g.,
/vendor).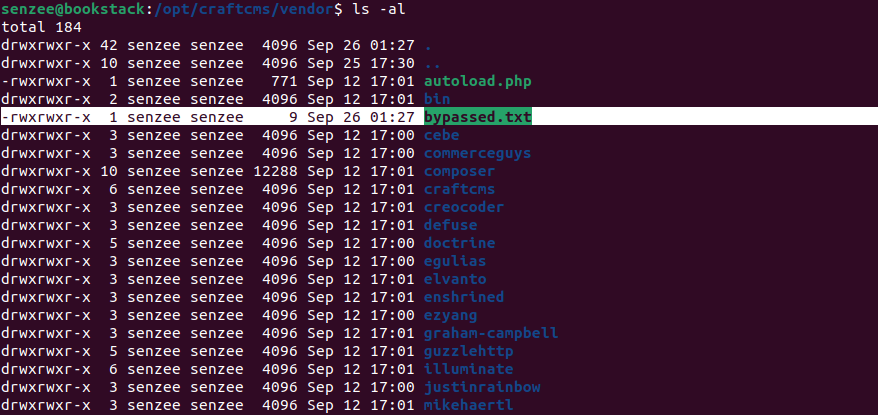
- SSTI payloads can be uploaded to
/templatesfolder, though full code execution was not achieved during testing, some payloads were still successful, leading to sensitive information disclosure, among other potential impacts.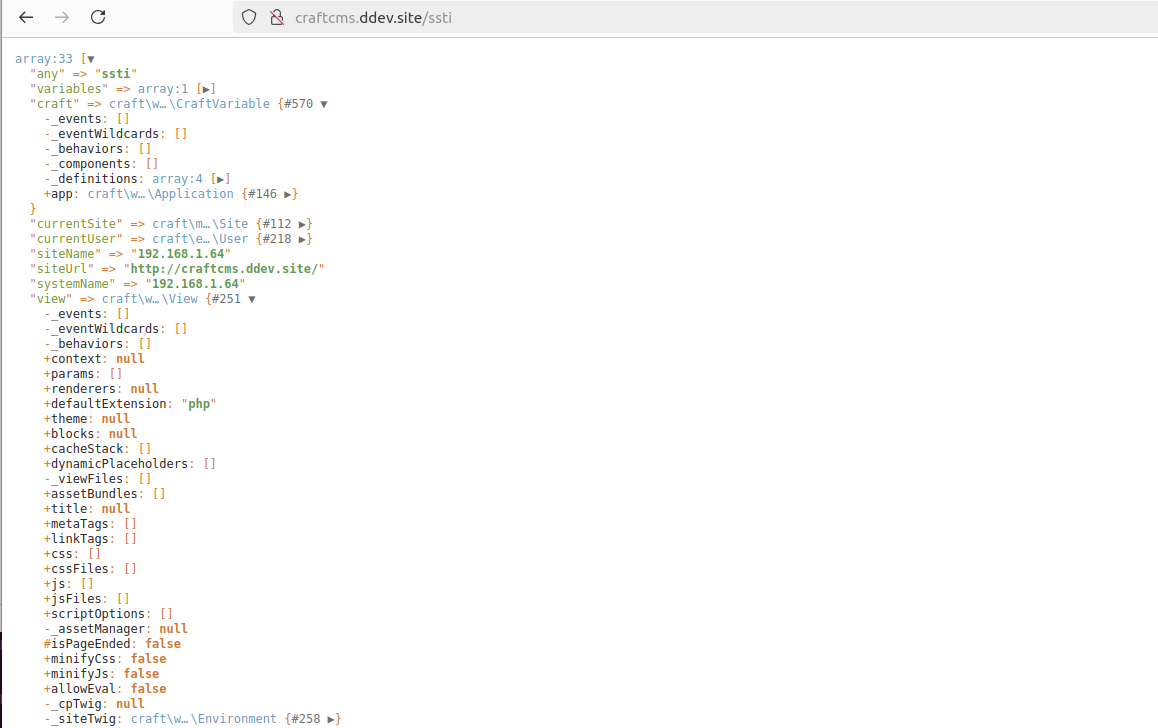
Impact
Attackers who compromise an admin account(The admin user is not equal to the server owner) can exploit this flaw to assign sensitive folders as the base path of the filesystem. For instance, if the path /templates is specified (e.g., file://file:////var/www/html/templates), the attacker could upload SSTI payloads. While CraftCMS includes strict SSTI input sanitization, RCE may still be possible if the attacker can craft a valid payload, as seen in similar vulnerabilities (e.g., GHSA-44wr-rmwq-3phw).
Additionally, attackers can upload tampered files to overwrite critical web application files. By enabling public URLs for files in the specified filesystem, they can also retrieve sensitive files (e.g., configuration files from the local file system).
Although the vulnerability is exploitable only in the authenticated users, configuration with ALLOW_ADMIN_CHANGES=true, there is still a potential security threat.
Affected packages
Start with the recorded fix for your release branch. Check your installed version and test compatibility before upgrading. Fixing this advisory does not rule out other vulnerabilities in the release.
From 5.0.0-RC1 before 5.4.6
Fixed in 5.4.6
57 explicitly affected versions
5.0.0, 5.0.0-RC1, 5.0.1, 5.0.2, 5.0.3, 5.0.4, 5.0.5, 5.0.6, 5.1.0, 5.1.1, 5.1.10, 5.1.2, 5.1.3, 5.1.4, 5.1.5, 5.1.6, 5.1.7, 5.1.8, 5.1.9, 5.2.0, 5.2.0-beta.1, 5.2.0-beta.2, 5.2.0-beta.3, 5.2.0-beta.4, 5.2.0-beta.5, 5.2.0-beta.6, 5.2.1, 5.2.10, 5.2.2, 5.2.3, 5.2.4, 5.2.4.1, 5.2.5, 5.2.6, 5.2.7, 5.2.8, 5.2.9, 5.3.0, 5.3.0-beta.1, 5.3.0-beta.2, 5.3.0.1, 5.3.0.2, 5.3.0.3, 5.3.1, 5.3.2, 5.3.3, 5.3.4, 5.3.5, 5.3.6, 5.4.0, 5.4.0.1, 5.4.1, 5.4.2, 5.4.3, 5.4.4, 5.4.5, 5.4.5.1
View affected-version evidence
{
  "ranges": [
    {
      "events": [
        {
          "introduced": "5.0.0-RC1"
        },
        {
          "fixed": "5.4.6"
        }
      ],
      "type": "ECOSYSTEM"
    }
  ],
  "versions": [
    "5.0.0",
    "5.0.0-RC1",
    "5.0.1",
    "5.0.2",
    "5.0.3",
    "5.0.4",
    "5.0.5",
    "5.0.6",
    "5.1.0",
    "5.1.1",
    "5.1.10",
    "5.1.2",
    "5.1.3",
    "5.1.4",
    "5.1.5",
    "5.1.6",
    "5.1.7",
    "5.1.8",
    "5.1.9",
    "5.2.0",
    "5.2.0-beta.1",
    "5.2.0-beta.2",
    "5.2.0-beta.3",
    "5.2.0-beta.4",
    "5.2.0-beta.5",
    "5.2.0-beta.6",
    "5.2.1",
    "5.2.10",
    "5.2.2",
    "5.2.3",
    "5.2.4",
    "5.2.4.1",
    "5.2.5",
    "5.2.6",
    "5.2.7",
    "5.2.8",
    "5.2.9",
    "5.3.0",
    "5.3.0-beta.1",
    "5.3.0-beta.2",
    "5.3.0.1",
    "5.3.0.2",
    "5.3.0.3",
    "5.3.1",
    "5.3.2",
    "5.3.3",
    "5.3.4",
    "5.3.5",
    "5.3.6",
    "5.4.0",
    "5.4.0.1",
    "5.4.1",
    "5.4.2",
    "5.4.3",
    "5.4.4",
    "5.4.5",
    "5.4.5.1"
  ]
}From 4.0.0-RC1 before 4.12.5
Fixed in 4.12.5
155 explicitly affected versions
4.0.0, 4.0.0-RC1, 4.0.0-RC2, 4.0.0-RC3, 4.0.0.1, 4.0.1, 4.0.2, 4.0.3, 4.0.4, 4.0.5, 4.0.5.1, 4.0.5.2, 4.0.6, 4.1.0, 4.1.0.1, 4.1.0.2, 4.1.1, 4.1.2, 4.1.3, 4.1.4, 4.1.4.1, 4.10.0, 4.10.0-beta.1, 4.10.0-beta.2, 4.10.1, 4.10.2, 4.10.3, 4.10.4, 4.10.5, 4.10.6, 4.10.7, 4.10.8, 4.11.0, 4.11.0.1, 4.11.0.2, 4.11.1, 4.11.2, 4.11.3, 4.11.4, 4.11.5, 4.12.0, 4.12.1, 4.12.2, 4.12.3, 4.12.4, 4.12.4.1, 4.2.0, 4.2.0.1, 4.2.0.2, 4.2.1, 4.2.1.1, 4.2.2, 4.2.3, 4.2.4, 4.2.5, 4.2.5.1, 4.2.5.2, 4.2.6, 4.2.7, 4.2.8, 4.3.0, 4.3.1, 4.3.10, 4.3.11, 4.3.2, 4.3.2.1, 4.3.3, 4.3.4, 4.3.5, 4.3.6, 4.3.6.1, 4.3.7, 4.3.7.1, 4.3.8, 4.3.8.1, 4.3.8.2, 4.3.9, 4.4.0, 4.4.0-beta.1, 4.4.0-beta.2, 4.4.0-beta.3, 4.4.0-beta.4, 4.4.0-beta.5, 4.4.0-beta.6, 4.4.0-beta.7, 4.4.1, 4.4.10, 4.4.10.1, 4.4.11, 4.4.12, 4.4.13, 4.4.14, 4.4.15, 4.4.16, 4.4.16.1, 4.4.17, 4.4.2, 4.4.3, 4.4.4, 4.4.5, 4.4.6, 4.4.6.1, 4.4.7, 4.4.7.1, 4.4.8, 4.4.9, 4.5.0, 4.5.0-beta.1, 4.5.0-beta.2, 4.5.1, 4.5.10, 4.5.11, 4.5.11.1, 4.5.12, 4.5.13, 4.5.14, 4.5.15, 4.5.2, 4.5.3, 4.5.4, 4.5.5, 4.5.6, 4.5.6.1, 4.5.7, 4.5.8, 4.5.9, 4.6.0, 4.6.0-RC1, 4.6.1, 4.7.0, 4.7.1, 4.7.2, 4.7.2.1, 4.7.3, 4.7.4, 4.8.0, 4.8.1, 4.8.10, 4.8.11, 4.8.2, 4.8.3, 4.8.4, 4.8.5, 4.8.6, 4.8.7, 4.8.8, 4.8.9, 4.9.0, 4.9.1, 4.9.2, 4.9.3, 4.9.4, 4.9.5, 4.9.6, 4.9.7
View affected-version evidence
{
  "ranges": [
    {
      "events": [
        {
          "introduced": "4.0.0-RC1"
        },
        {
          "fixed": "4.12.5"
        }
      ],
      "type": "ECOSYSTEM"
    }
  ],
  "versions": [
    "4.0.0",
    "4.0.0-RC1",
    "4.0.0-RC2",
    "4.0.0-RC3",
    "4.0.0.1",
    "4.0.1",
    "4.0.2",
    "4.0.3",
    "4.0.4",
    "4.0.5",
    "4.0.5.1",
    "4.0.5.2",
    "4.0.6",
    "4.1.0",
    "4.1.0.1",
    "4.1.0.2",
    "4.1.1",
    "4.1.2",
    "4.1.3",
    "4.1.4",
    "4.1.4.1",
    "4.10.0",
    "4.10.0-beta.1",
    "4.10.0-beta.2",
    "4.10.1",
    "4.10.2",
    "4.10.3",
    "4.10.4",
    "4.10.5",
    "4.10.6",
    "4.10.7",
    "4.10.8",
    "4.11.0",
    "4.11.0.1",
    "4.11.0.2",
    "4.11.1",
    "4.11.2",
    "4.11.3",
    "4.11.4",
    "4.11.5",
    "4.12.0",
    "4.12.1",
    "4.12.2",
    "4.12.3",
    "4.12.4",
    "4.12.4.1",
    "4.2.0",
    "4.2.0.1",
    "4.2.0.2",
    "4.2.1",
    "4.2.1.1",
    "4.2.2",
    "4.2.3",
    "4.2.4",
    "4.2.5",
    "4.2.5.1",
    "4.2.5.2",
    "4.2.6",
    "4.2.7",
    "4.2.8",
    "4.3.0",
    "4.3.1",
    "4.3.10",
    "4.3.11",
    "4.3.2",
    "4.3.2.1",
    "4.3.3",
    "4.3.4",
    "4.3.5",
    "4.3.6",
    "4.3.6.1",
    "4.3.7",
    "4.3.7.1",
    "4.3.8",
    "4.3.8.1",
    "4.3.8.2",
    "4.3.9",
    "4.4.0",
    "4.4.0-beta.1",
    "4.4.0-beta.2",
    "4.4.0-beta.3",
    "4.4.0-beta.4",
    "4.4.0-beta.5",
    "4.4.0-beta.6",
    "4.4.0-beta.7",
    "4.4.1",
    "4.4.10",
    "4.4.10.1",
    "4.4.11",
    "4.4.12",
    "4.4.13",
    "4.4.14",
    "4.4.15",
    "4.4.16",
    "4.4.16.1",
    "4.4.17",
    "4.4.2",
    "4.4.3",
    "4.4.4",
    "4.4.5",
    "4.4.6",
    "4.4.6.1",
    "4.4.7",
    "4.4.7.1",
    "4.4.8",
    "4.4.9",
    "4.5.0",
    "4.5.0-beta.1",
    "4.5.0-beta.2",
    "4.5.1",
    "4.5.10",
    "4.5.11",
    "4.5.11.1",
    "4.5.12",
    "4.5.13",
    "4.5.14",
    "4.5.15",
    "4.5.2",
    "4.5.3",
    "4.5.4",
    "4.5.5",
    "4.5.6",
    "4.5.6.1",
    "4.5.7",
    "4.5.8",
    "4.5.9",
    "4.6.0",
    "4.6.0-RC1",
    "4.6.1",
    "4.7.0",
    "4.7.1",
    "4.7.2",
    "4.7.2.1",
    "4.7.3",
    "4.7.4",
    "4.8.0",
    "4.8.1",
    "4.8.10",
    "4.8.11",
    "4.8.2",
    "4.8.3",
    "4.8.4",
    "4.8.5",
    "4.8.6",
    "4.8.7",
    "4.8.8",
    "4.8.9",
    "4.9.0",
    "4.9.1",
    "4.9.2",
    "4.9.3",
    "4.9.4",
    "4.9.5",
    "4.9.6",
    "4.9.7"
  ]
}