
Twig Sandbox Escape by authenticated users with access to editing CMS templates when safemode is enabled.
The advisory, in context
Impact
An authenticated backend user with the cms.manage_pages, cms.manage_layouts, or cms.manage_partials permissions who would normally not be permitted to provide PHP code to be executed by the CMS due to cms.enableSafeMode being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP.
This is not a problem for anyone that trusts their users with those permissions to normally write & manage PHP within the CMS by not having cms.enableSafeMode enabled, but would be a problem for anyone relying on cms.enableSafeMode to ensure that users with those permissions in production do not have access to write & execute arbitrary PHP.
Patches
Issue has been patched in Build 469 (v1.0.469) and v1.1.0.
Workarounds
Apply https://github.com/octobercms/october/compare/106daa2930de4cebb18732732d47d4056f01dd5b...7cb148c1677373ac30ccfd3069d18098e403e1ca to your installation manually if unable to upgrade to Build 469.
References
Reported by ka1n4t
For more information
If you have any questions or comments about this advisory:
- Email us at hello@octobercms.com
Threat assessment:
<img width="1108" alt="Screen Shot 2020-10-10 at 1 21 13 PM" src="https://user-images.githubusercontent.com/7253840/95663316-7de28b80-0afb-11eb-999d-a6526cf78709.png">
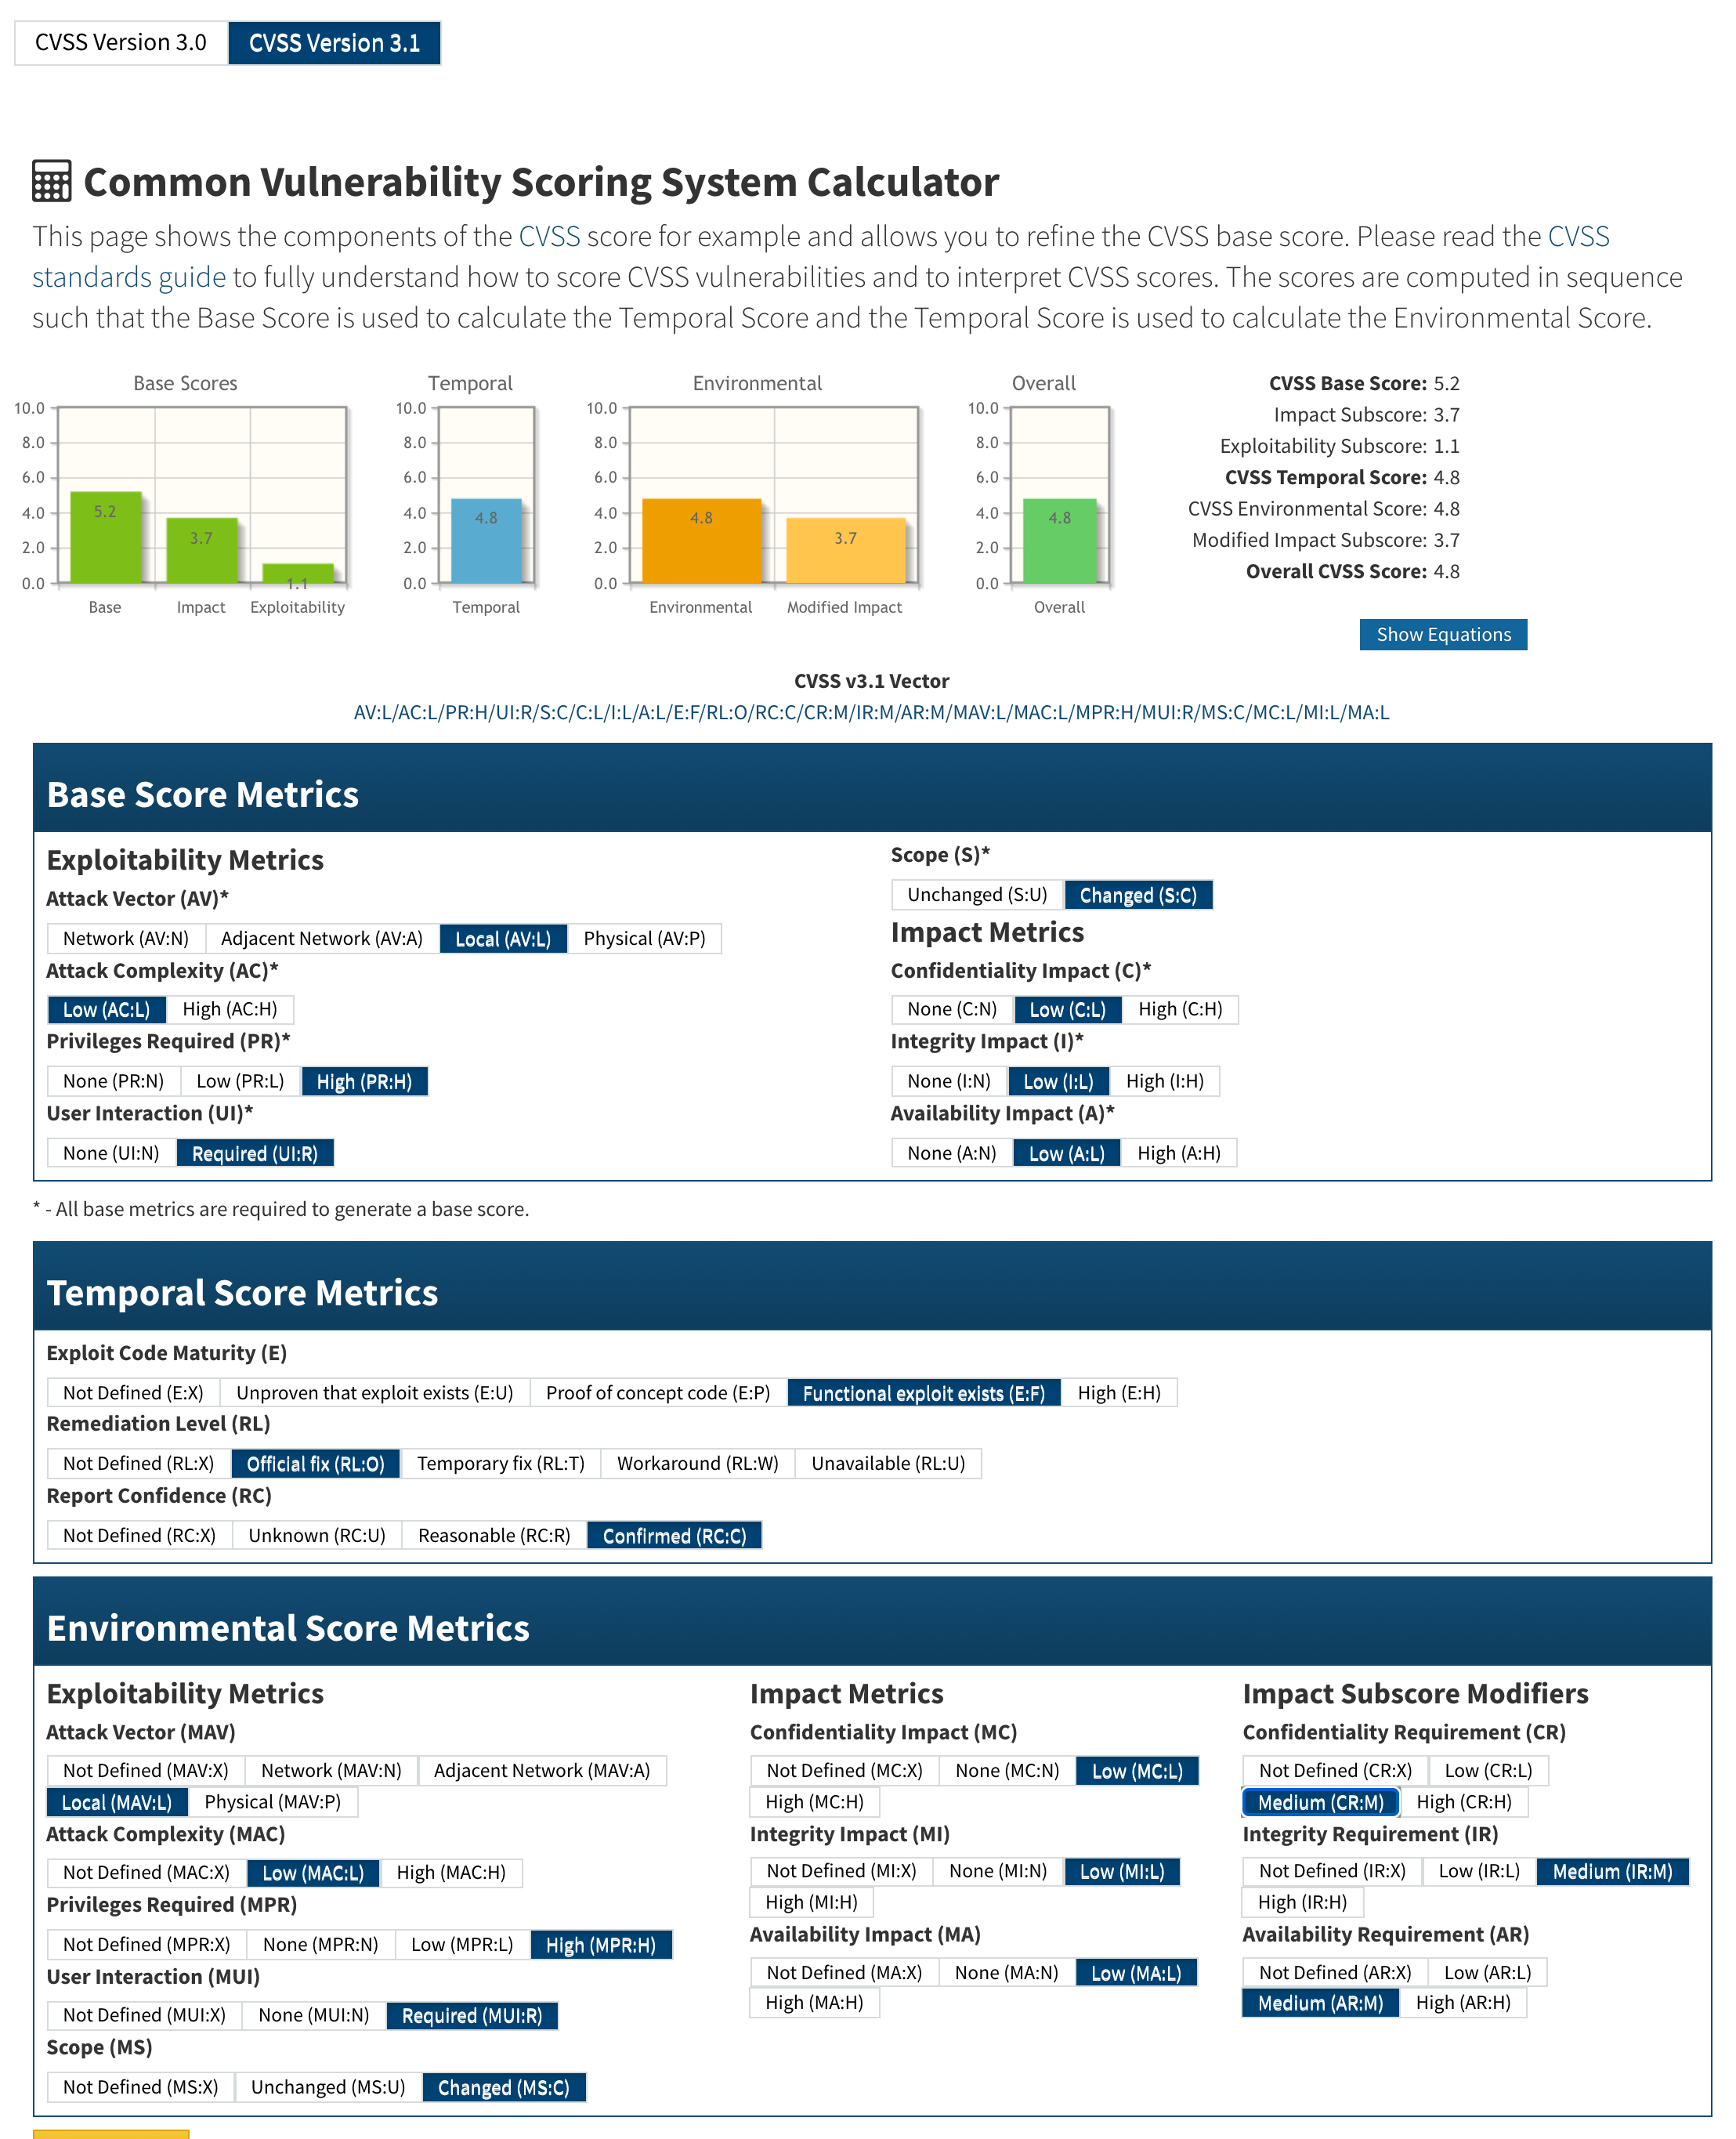
Affected packages
Start with the recorded fix for your release branch. Check your installed version and test compatibility before upgrading. Fixing this advisory does not rule out other vulnerabilities in the release.
From 1.0.319 before 1.0.469
Fixed in 1.0.469
150 explicitly affected versions
v1.0.319, v1.0.320, v1.0.321, v1.0.322, v1.0.323, v1.0.324, v1.0.325, v1.0.326, v1.0.327, v1.0.328, v1.0.329, v1.0.330, v1.0.331, v1.0.332, v1.0.333, v1.0.334, v1.0.335, v1.0.336, v1.0.337, v1.0.338, v1.0.339, v1.0.340, v1.0.341, v1.0.342, v1.0.343, v1.0.344, v1.0.345, v1.0.346, v1.0.347, v1.0.348, v1.0.349, v1.0.350, v1.0.351, v1.0.352, v1.0.353, v1.0.354, v1.0.355, v1.0.356, v1.0.357, v1.0.358, v1.0.359, v1.0.360, v1.0.361, v1.0.362, v1.0.363, v1.0.364, v1.0.365, v1.0.366, v1.0.367, v1.0.368, v1.0.369, v1.0.370, v1.0.371, v1.0.372, v1.0.373, v1.0.374, v1.0.375, v1.0.376, v1.0.377, v1.0.378, v1.0.379, v1.0.380, v1.0.381, v1.0.382, v1.0.383, v1.0.384, v1.0.385, v1.0.386, v1.0.387, v1.0.388, v1.0.389, v1.0.390, v1.0.391, v1.0.392, v1.0.393, v1.0.394, v1.0.395, v1.0.396, v1.0.397, v1.0.398, v1.0.399, v1.0.400, v1.0.401, v1.0.402, v1.0.403, v1.0.404, v1.0.405, v1.0.406, v1.0.407, v1.0.408, v1.0.409, v1.0.410, v1.0.411, v1.0.412, v1.0.413, v1.0.414, v1.0.415, v1.0.416, v1.0.417, v1.0.418, v1.0.419, v1.0.420, v1.0.421, v1.0.422, v1.0.423, v1.0.424, v1.0.425, v1.0.426, v1.0.427, v1.0.428, v1.0.429, v1.0.430, v1.0.431, v1.0.432, v1.0.433, v1.0.434, v1.0.435, v1.0.436, v1.0.437, v1.0.438, v1.0.439, v1.0.440, v1.0.441, v1.0.442, v1.0.443, v1.0.444, v1.0.445, v1.0.446, v1.0.447, v1.0.448, v1.0.449, v1.0.450, v1.0.451, v1.0.452, v1.0.453, v1.0.454, v1.0.455, v1.0.456, v1.0.457, v1.0.458, v1.0.459, v1.0.460, v1.0.461, v1.0.462, v1.0.463, v1.0.464, v1.0.465, v1.0.466, v1.0.467, v1.0.468
View affected-version evidence
{
  "ranges": [
    {
      "events": [
        {
          "introduced": "1.0.319"
        },
        {
          "fixed": "1.0.469"
        }
      ],
      "type": "ECOSYSTEM"
    }
  ],
  "versions": [
    "v1.0.319",
    "v1.0.320",
    "v1.0.321",
    "v1.0.322",
    "v1.0.323",
    "v1.0.324",
    "v1.0.325",
    "v1.0.326",
    "v1.0.327",
    "v1.0.328",
    "v1.0.329",
    "v1.0.330",
    "v1.0.331",
    "v1.0.332",
    "v1.0.333",
    "v1.0.334",
    "v1.0.335",
    "v1.0.336",
    "v1.0.337",
    "v1.0.338",
    "v1.0.339",
    "v1.0.340",
    "v1.0.341",
    "v1.0.342",
    "v1.0.343",
    "v1.0.344",
    "v1.0.345",
    "v1.0.346",
    "v1.0.347",
    "v1.0.348",
    "v1.0.349",
    "v1.0.350",
    "v1.0.351",
    "v1.0.352",
    "v1.0.353",
    "v1.0.354",
    "v1.0.355",
    "v1.0.356",
    "v1.0.357",
    "v1.0.358",
    "v1.0.359",
    "v1.0.360",
    "v1.0.361",
    "v1.0.362",
    "v1.0.363",
    "v1.0.364",
    "v1.0.365",
    "v1.0.366",
    "v1.0.367",
    "v1.0.368",
    "v1.0.369",
    "v1.0.370",
    "v1.0.371",
    "v1.0.372",
    "v1.0.373",
    "v1.0.374",
    "v1.0.375",
    "v1.0.376",
    "v1.0.377",
    "v1.0.378",
    "v1.0.379",
    "v1.0.380",
    "v1.0.381",
    "v1.0.382",
    "v1.0.383",
    "v1.0.384",
    "v1.0.385",
    "v1.0.386",
    "v1.0.387",
    "v1.0.388",
    "v1.0.389",
    "v1.0.390",
    "v1.0.391",
    "v1.0.392",
    "v1.0.393",
    "v1.0.394",
    "v1.0.395",
    "v1.0.396",
    "v1.0.397",
    "v1.0.398",
    "v1.0.399",
    "v1.0.400",
    "v1.0.401",
    "v1.0.402",
    "v1.0.403",
    "v1.0.404",
    "v1.0.405",
    "v1.0.406",
    "v1.0.407",
    "v1.0.408",
    "v1.0.409",
    "v1.0.410",
    "v1.0.411",
    "v1.0.412",
    "v1.0.413",
    "v1.0.414",
    "v1.0.415",
    "v1.0.416",
    "v1.0.417",
    "v1.0.418",
    "v1.0.419",
    "v1.0.420",
    "v1.0.421",
    "v1.0.422",
    "v1.0.423",
    "v1.0.424",
    "v1.0.425",
    "v1.0.426",
    "v1.0.427",
    "v1.0.428",
    "v1.0.429",
    "v1.0.430",
    "v1.0.431",
    "v1.0.432",
    "v1.0.433",
    "v1.0.434",
    "v1.0.435",
    "v1.0.436",
    "v1.0.437",
    "v1.0.438",
    "v1.0.439",
    "v1.0.440",
    "v1.0.441",
    "v1.0.442",
    "v1.0.443",
    "v1.0.444",
    "v1.0.445",
    "v1.0.446",
    "v1.0.447",
    "v1.0.448",
    "v1.0.449",
    "v1.0.450",
    "v1.0.451",
    "v1.0.452",
    "v1.0.453",
    "v1.0.454",
    "v1.0.455",
    "v1.0.456",
    "v1.0.457",
    "v1.0.458",
    "v1.0.459",
    "v1.0.460",
    "v1.0.461",
    "v1.0.462",
    "v1.0.463",
    "v1.0.464",
    "v1.0.465",
    "v1.0.466",
    "v1.0.467",
    "v1.0.468"
  ]
}